Go deploys
Deploy Go applications to your own server
Ship a Go service to a server you control without stitching together a build script, a process manager, and a reverse proxy. Phelix owns the path from source to serving traffic, in one CLI.
Released Phelix hosts: Linux and macOS. Builds Go and Rust with your host toolchain.
simulated
go module
one command compiles the module into a numbered build
From source to a versioned binary
One command compiles your Go module into an immutable, numbered build.
Phelix builds native Go binaries directly on the host using the installed Go toolchain, or the latest toolchain when none is present, with no container step required. Every build is a numbered version paired with a build report and an encrypted environment snapshot, so you always know exactly what is running and can return to it later. The full command set, the interactive wizard, and the lifecycle verbs live in build and lifecycle. For the model behind it all, start with the overview.
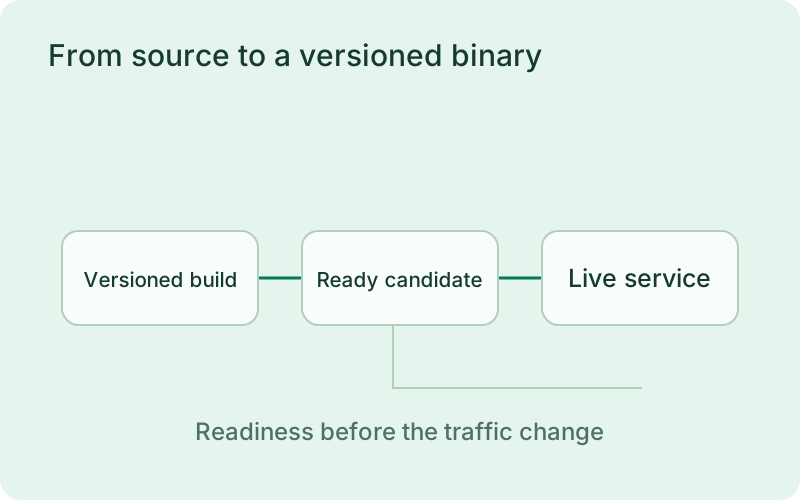
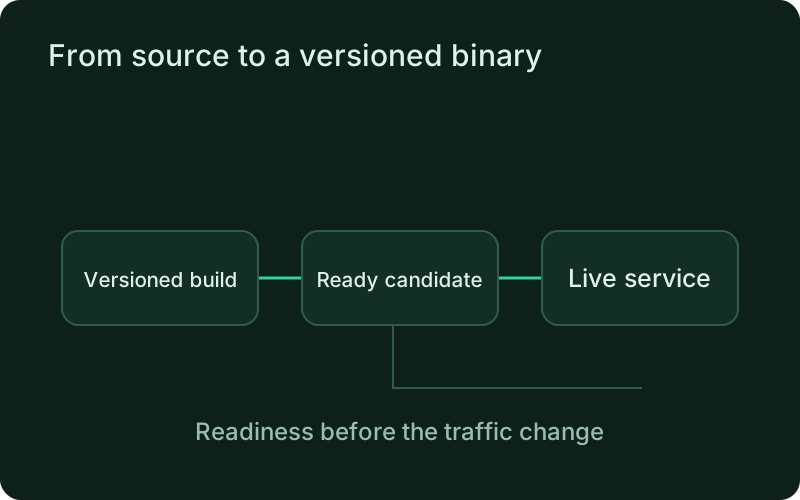
For a customer-facing API or an internal service, a numbered release makes the deployment easier to review and recover. Confirm that the build result belongs to the revision you intended to ship, and keep the previous working artifact available. This gives the person operating the service a concrete release record instead of a loose binary copied onto the server.
phelix buildDeploy the exact commit
Push to deploy, or run the deploy yourself. Either way, the binary that serves traffic is the one you built.
Wire an HMAC-authenticated Git webhook and Phelix deploys the exact pushed commit, with durable jobs and restart recovery, as described in Git webhook deploys. Or run the deploy by hand and pick the strategy that fits the service. Classic, blue-green, rolling, and canary are all covered in deployment strategies. Classic is a stop then start and can drop traffic briefly; the proxy-based strategies do not.
Release the revision that was reviewed, then check that the running application reports the expected version. A signed webhook protects the incoming request, while the selected deployment strategy determines how customers move to the new instance. Review both the source identity and the readiness result so an automated trigger does not become an unexamined production change.
phelix deploy api --blue-greenHealth-gated cutover, and a way back
Traffic moves to a new version only after it passes its checks, and every version stays one command from rollback.
On proxy-based deploys, Phelix starts the new version, health-checks it, and switches the host-local HTTP proxy only when it is ready. If a deploy goes wrong, roll back to a retained version through the same topology. The mechanics are in zero-downtime deployment for Go and the versions and rollback docs. Health checks reduce risk; they do not prove that every behavior of your application is correct. Treat them as a gate, not a guarantee.
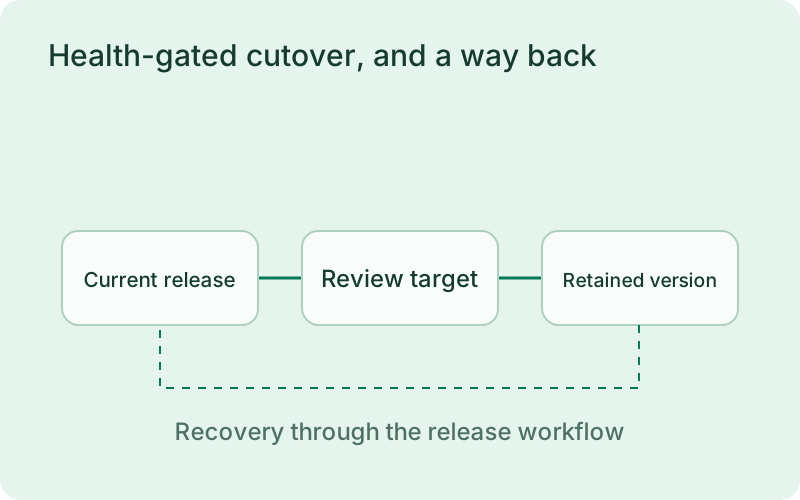
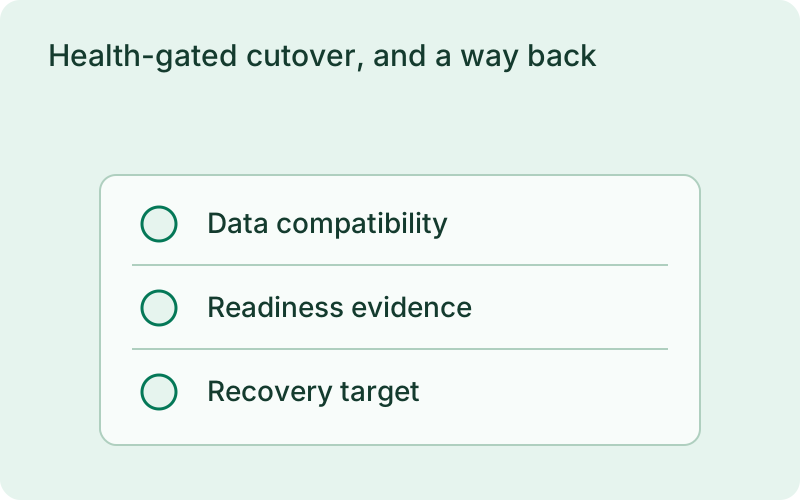
Check the customer journey that matters after the traffic switch, such as signing in or completing a request against the database. Readiness protects the moment a candidate joins service, but a later behavioral problem may still require recovery. Keep database changes compatible with the retained release so restoring the application remains a useful option.
Where it runs
Phelix operates applications on infrastructure you already have.
Released Phelix hosts run on Linux and macOS, and the whole tool is a single binary with no Kubernetes to operate. Phelix does not provision the server: you bring the machine, the network, and TLS, and Phelix takes over at build, deploy, health, and rollback. Environment values are encrypted at rest with AES-256-GCM using a local key. That is encrypted local storage, not a remote secrets vault; see environment and security for the model.
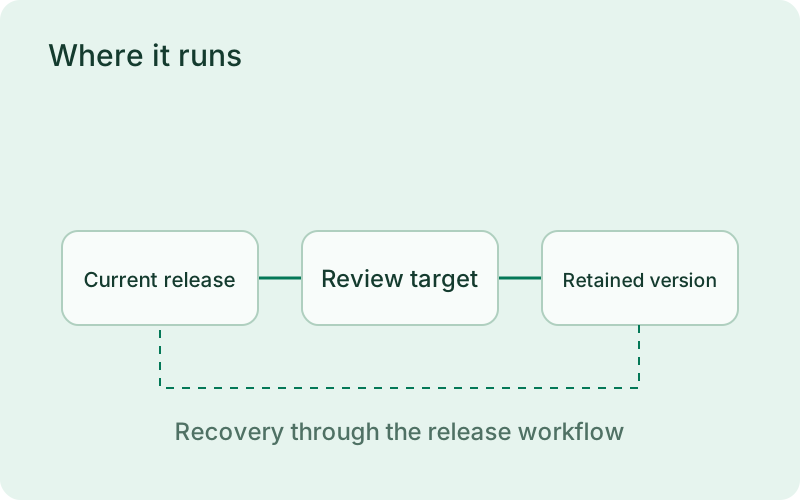
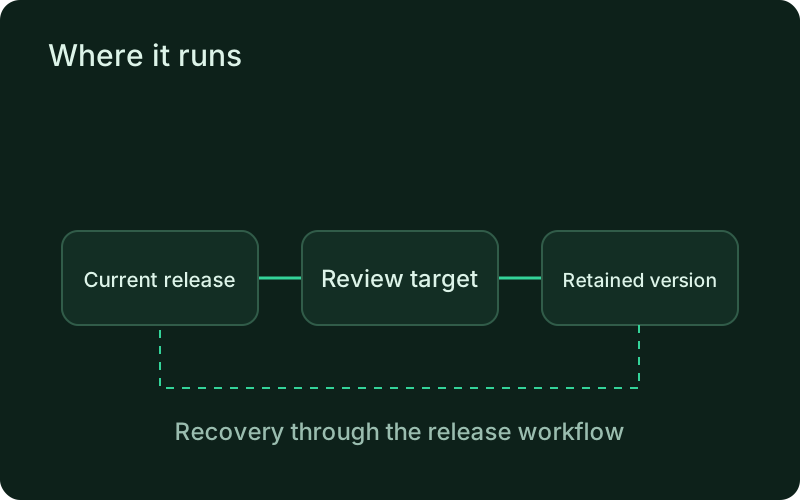
Choose a host with enough room for both the live service and the candidate during an update. Plan backups, firewall rules, and certificate renewal as part of operating that machine. Phelix manages the application lifecycle on the server you provide; availability of the host and the surrounding infrastructure still needs its own practical recovery plan.
Deploy from a coding agent
New in v1.1.0: hand the deploy to Claude Code or Codex, safely.
Phelix ships a built-in MCP adapter so a coding agent can propose a Go deploy as an immutable plan and apply it over the same pipeline the CLI uses. Every change is gated by a fail-closed execution-authorization boundary with plan-bound approvals, and tracked end to end with agent execution sessions, so nothing deploys that a human did not sign off.
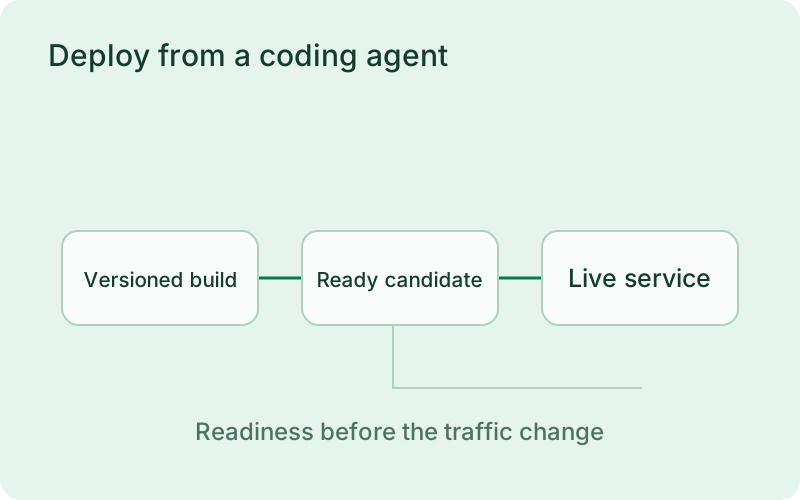
The assistant can help prepare a release while you keep responsibility for the production decision. Review the application and action in the proposed plan before approving it. If the plan does not match the intended change, request a replacement. After an approved release, check the live service just as you would after a release started manually.
One binary between git push and production.
Install the CLI, verify the host, and follow the quick start to build your first application.