Rust deploys
Deploy Rust applications to your own server
Take a Rust release binary from build to serving traffic on a server you control. Phelix compiles, deploys with health-gated cutover, supervises, and rolls back, from one CLI.
Released Phelix hosts: Linux and macOS. Builds Go and Rust with your host toolchain.
simulated
the release build starts from the toolchain already installed
Build the release binary, versioned
Phelix compiles Rust stable directly on the host into an immutable, numbered build.
A Rust binary deployment tool should treat the compiled artifact as the unit of delivery. Phelix builds Rust stable applications natively, with no container required, and pairs every numbered build with a build report and an encrypted environment snapshot. What Phelix is and how the build fits the wider lifecycle is covered in the overview and build and lifecycle docs.
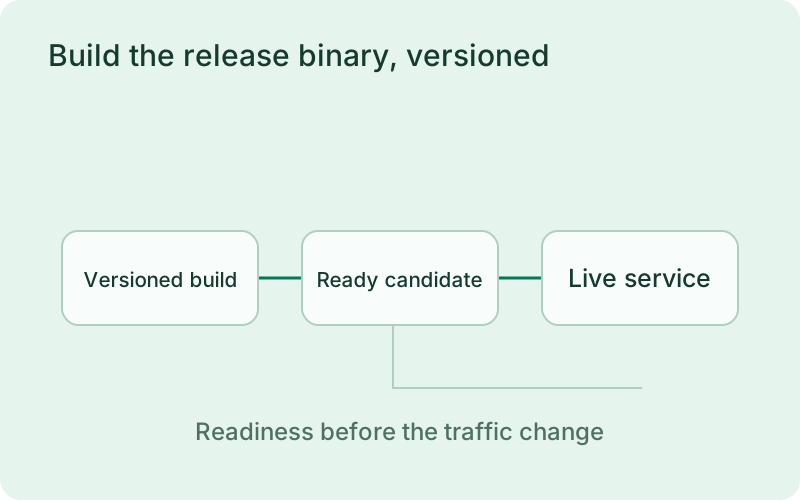
A versioned release is useful for Rust services with a native toolchain and system-library requirements. Confirm the destination environment before building and retain the resulting artifact with its release record. During recovery, a known binary is easier to restore than a hurried rebuild whose toolchain or dependencies may have changed since the last successful release.
phelix buildShip it without dropping traffic
Choose a deployment strategy, and let health checks gate the cutover.
Phelix offers classic, blue-green, rolling, and canary deployments, detailed in deployment strategies. On proxy-based strategies it starts the new version, health-checks it, and switches the host-local proxy only once it is ready. Classic deployment is a stop then start and can have brief downtime; the proxy strategies avoid it. The full approach for a Rust or Go service is walked through in zero-downtime deployment for Go, and it applies the same way to Rust.
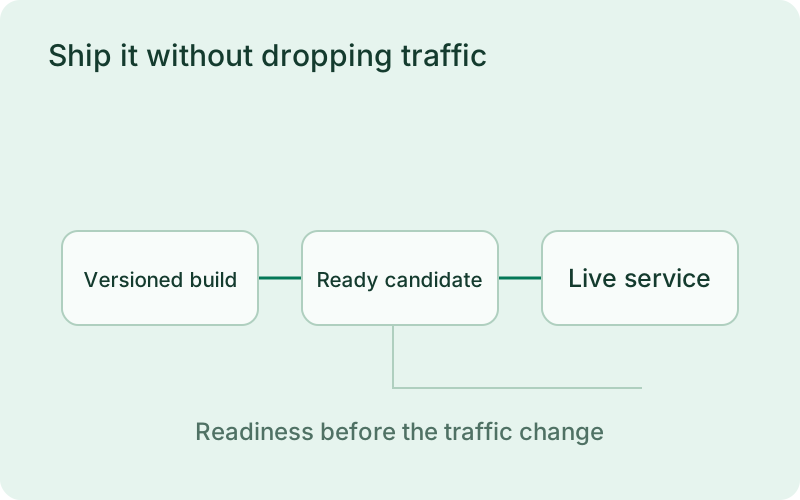
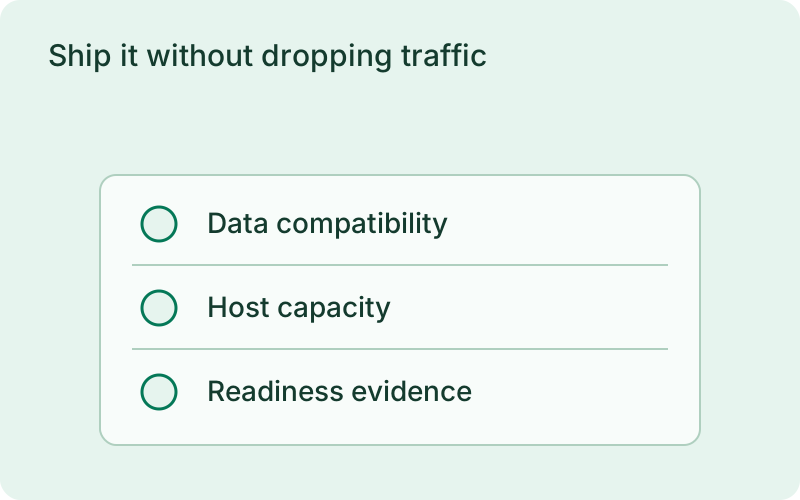
Allow capacity for the old and new instances to overlap, and test that the readiness endpoint reflects the dependencies needed by real requests. Review how the service handles shutdown and long connections so draining gives existing work time to finish. The traffic switch protects availability during a release; it does not correct incompatible changes in shared data.
phelix deploy edge --rollingSupervise, observe, and roll back
After deploy, Phelix keeps the process healthy and one command from a known-good version.
Phelix supervises the running process per host, streams metrics and redacted logs to an optional dashboard, and can roll back to any retained version through the current deployment topology. Released hosts run on Linux and macOS, and Phelix operates on infrastructure you already control rather than provisioning it. Environment values are encrypted at rest with AES-256-GCM using a local key: encrypted local storage, not a remote vault. The details are in environment and security.
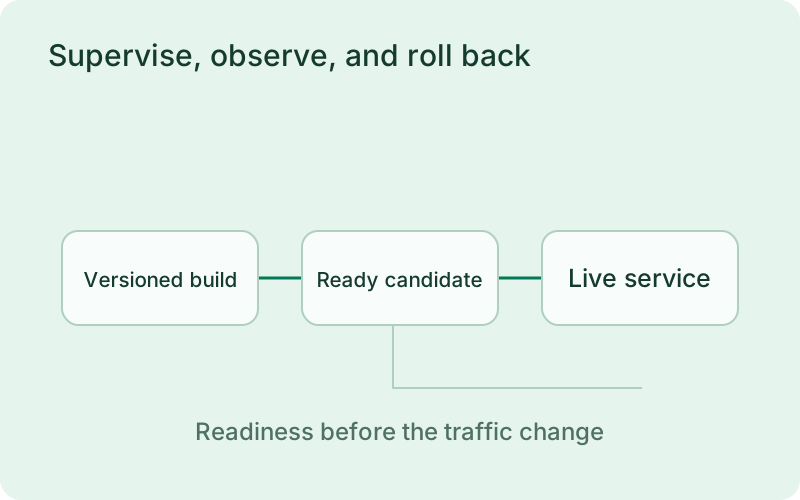
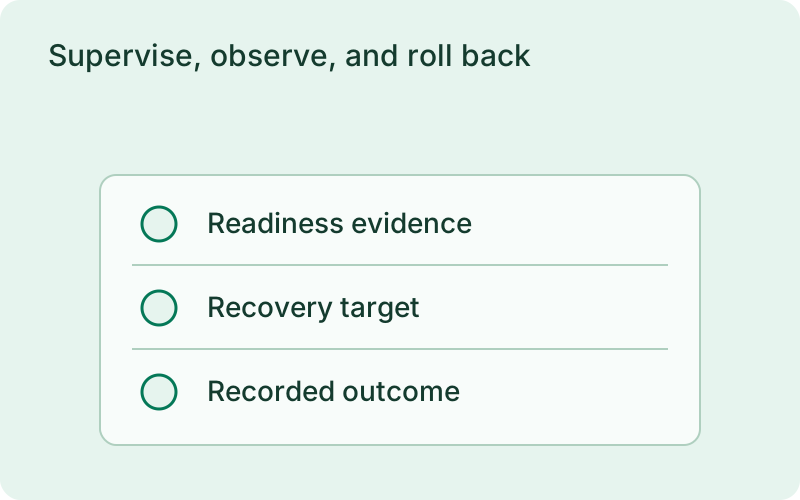
Use process state, health results, and logs together when investigating a failed release. A service that is running can still be failing one customer operation or waiting on an external provider. Confirm the affected behavior after any restart or rollback, and keep the recovery notes tied to the version that caused the problem and the version that restored service.
Deploy from a coding agent
New in v1.1.0: Phelix is a controlled execution layer for coding agents.
A built-in MCP adapter lets Claude Code or Codex propose a Rust deploy as an immutable, content-addressed plan and apply it through the exact pipeline the CLI uses. A fail-closed execution-authorization boundary keeps every apply plan-bound and human-approved, and agent execution sessions track the work so an interrupted agent resumes by reading state.
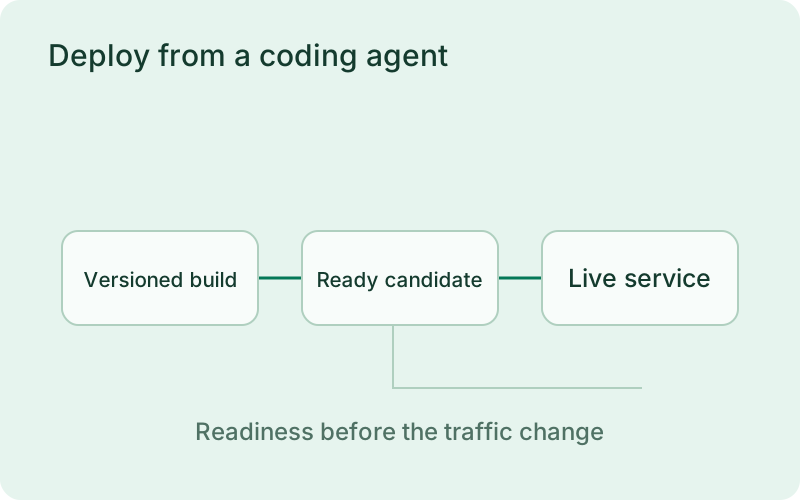
An assistant-driven release should still be a specific, reviewable operating change. Inspect the proposed application, target, and action, then approve that exact plan through the supported human workflow. The host enforces authorization while the normal release pipeline verifies readiness. Review the service afterward rather than treating authorization or command completion as proof of customer success.
One binary between git push and production.
Install the CLI, verify the host, and follow the quick start to build your first application.